Provably fair is the crypto casino’s answer to the question of trust. Instead of asking you to believe a testing lab, it hands you the maths and invites you to check the result yourself. That is a genuinely clever idea, it works, and what it establishes is much narrower than the marketing around it suggests.
What Is Provably Fair in Online Casinos?


The short answer: Before the round, the casino publishes a hash of a secret it has already chosen. After the round, it reveals the secret. You hash the revealed secret and compare. If they match, the result was fixed before you bet and was not changed afterwards. That is the entire claim.
How the Scheme Works
BGaming documents its own version in plain terms, and it is the standard shape of the mechanism.
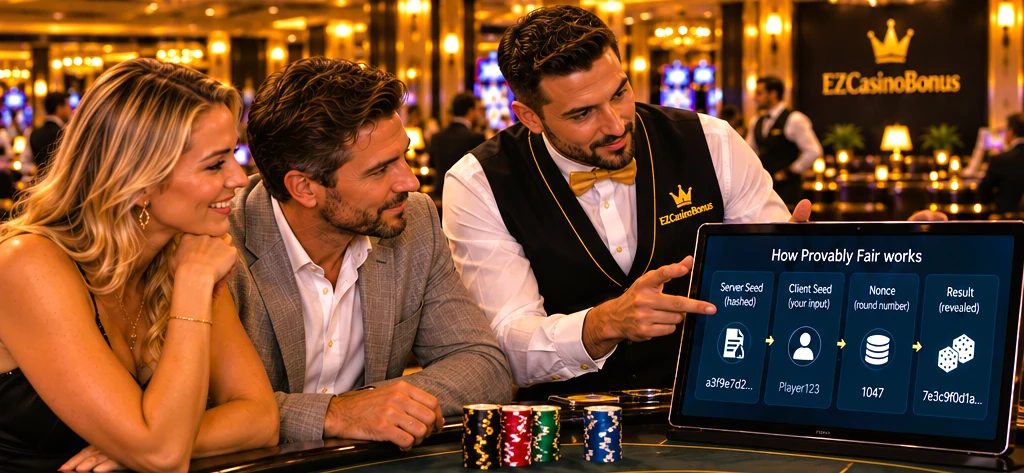
- The game calculates the outcome for the round and generates a random secret string
- The outcome and the secret are hashed together with SHA-256, and that hash is given to you before you bet
- You can supply your own client seed, which mixes your input into the result so the operator cannot have pre-computed it against you alone
- A nonce, a counter that increments with each bet, keeps every round in a series distinct
- After the round, the secret and the result are revealed, and you can hash them yourself and check they produce the hash you were given
BGaming states what this establishes: that “the outcome of the round is unaffected by the player’s bet and that player cannot know the outcome before the actual gameplay”. That is an accurate and appropriately modest claim, which is more than can be said for how the feature is usually marketed.
The Three Things It Does Not Prove
Each of the three matters, and they fail in different directions.
| What people assume it proves | What it actually proves |
|---|---|
| The game returns the advertised RTP | Nothing about the return. The rule turning a hash into an outcome can embed any house edge and still verify perfectly every time |
| The randomness itself is honest | Only that the committed value was not changed. It says nothing about how that value was generated, or whether a default client seed you never touched is genuinely neutral |
| The casino is trustworthy | Nothing about the operator. A casino with a flawless implementation can still refuse withdrawals, freeze accounts or disappear with deposits |
The one to internalise: Verification confirms the result was not tampered with after your bet. It does not confirm the game was worth betting on. Those are different questions and only the second one determines what the game costs you.
Why Regulators Do Not Accept It Instead
Because it answers a different question from the one certification answers.
The UK’s technical standard on random outcomes requires randomness to be demonstrated “through, for example, statistical analysis using generally accepted tests and methods of analysis”. That is a statistical claim about the distribution of results over many rounds. Provably fair is a cryptographic claim about a single round’s integrity. One does not substitute for the other, and the standard makes no reference to cryptographic self-verification at any point.
No licensed jurisdiction was found accepting provably fair in place of a lab certificate. Curacao, historically the most permissive route for self-certified crypto casinos, moved the other way in its recent reform, abolishing the master licence structure and requiring direct licensees to obtain independent certification of their game content and random number generator. What certification actually covers, and what it also does not, is in RNG certification and testing labs.
The Two Are Complements, Not Rivals
| Lab certification | Provably fair | |
|---|---|---|
| What it checks | That the generator is statistically random and the game’s maths matches its stated return | That this specific round’s result was committed before your bet |
| Scope | Many rounds, one build | One round, in real time |
| Who checks | An accredited lab, before launch | You, afterwards |
| Its weakness | It is a snapshot of a build, not of the live game | It says nothing about the return or about the operator |
Read that table and the answer becomes obvious. The strongest position is a licensed operator with certified games that also publishes verification. The weakest is a site with verification and no licence, which is where the feature is most heavily advertised, and which is the situation described in licensed versus offshore casinos.
Where You Will Meet It
Mostly in crypto facing casinos and in the studios that supply them. BGaming publishes its scheme and applies it across its catalogue. Spribe’s Aviator uses a multi seed variant, described as combining the server’s seed with seeds from the first three players in a round before publishing the hash, though that description comes from an independent explainer rather than Spribe’s own documentation. Many crypto casinos run comparable schemes on their in house games. Crypto bonuses frequently sit on exactly these games, which is worth knowing before you judge an offer by its size.
Crash games are where players encounter it most, since a rising multiplier with a hidden stopping point is exactly the format where “was that fixed after I bet?” is the natural suspicion. The format itself is worth understanding first.
The habit worth building: Verify one bet, once, on any provably fair game you play regularly. Not because you expect a discrepancy, but because a site that makes verification awkward, hides the tool, or does not reveal the seed on request has told you something the marketing did not.
How to Actually Verify
Every implementation differs, and the shape is consistent. Find the fairness or verify option, usually in the game menu or your account settings. Note the hash you were given before the round. After the round, take the revealed server seed, your client seed and the nonce, run them through the verifier the casino provides or an independent one, and confirm you get the same hash and the same result.
Changing your client seed periodically is worth doing, since it is the one input you control and a default you never touched is the part of the scheme you are trusting rather than checking.
How Much Weight to Give Provably Fair
Treat provably fair as a real feature answering a small question well. It is better than nothing and it is not a substitute for a licence, because no regulator treats it as one and because the failures players actually suffer, refused withdrawals and unreachable support, are not failures it can detect. Use the licence as the filter, the RTP figure as the decision and verification as the audit, in that order. Crypto casinos that hold a real licence are where all three are available at once.
Frequently Asked Questions
The casino chooses the result and a secret before the round, hashes them together with SHA-256 and gives you that hash before you bet. After the round it reveals the secret and the result. You hash them yourself and compare. A match proves the result existed before your bet and was not changed.
The server seed is the operator’s secret input, committed in advance as a hash. The client seed is your input, which mixes into the calculation so the operator cannot pre-compute a result aimed at you specifically. A nonce, an incrementing counter, keeps successive rounds distinct.
It can still do everything except change a result after your bet. The mapping from hash to outcome can embed any house edge and still verify perfectly, the seed generation itself is not proven honest, and no cryptographic scheme prevents an operator refusing to pay a withdrawal.
It answers a different question. Certification is a statistical claim about how a generator behaves across many rounds and whether the maths matches the advertised return. Provably fair is a cryptographic claim about one round’s integrity. The strongest position has both, and neither replaces the other.
None was found accepting it in place of independent laboratory certification. The UK’s technical standard requires randomness to be demonstrated through statistical analysis using generally accepted tests, and does not mention cryptographic self-verification at all. Curacao’s recent reform moved toward requiring independent certification rather than away from it.
Find the fairness or verify option in the game menu or your account settings. Note the hash given before the round, then after it take the revealed server seed, your client seed and the nonce, run them through the verifier and confirm you get the same hash and the same result.
Periodically, yes. It is the only input you control, and a default seed you have never touched is a part of the scheme you are trusting rather than verifying. Changing it costs nothing and removes the weakest assumption in the setup.
No, and this is the most common misunderstanding. Verification confirms the result was not tampered with. It says nothing about what the game returns over time, which is set by the paytable and the rule turning the hash into an outcome, and which needs the same RTP figure any other game would.